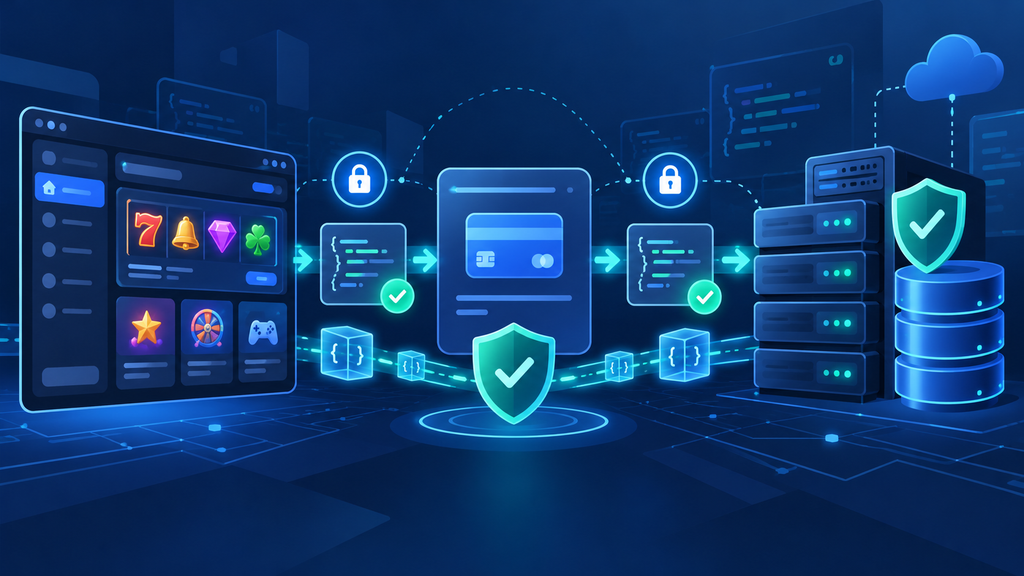
Casino site webhook security protects automated notifications exchanged between online gaming platforms, payment processors, and connected services. It uses cryptographic signatures, HTTPS encryption, event validation, and duplicate detection to prevent unauthorized messages from triggering financial or account changes.
A secure webhook handler verifies the sender, checks incoming data integrity, and confirms that a transaction has not already been processed before updating application records. These safeguards help prevent forged payment confirmations, replay attacks, and duplicate transaction processing.
Key Takeaways
- Signature verification confirms that incoming notifications originate from an authorized sender and have not been modified.
- HTTPS encryption protects webhook data during transmission.
- Replay protection helps detect previously submitted or outdated notifications.
- Idempotency controls prevent repeated notifications from producing duplicate financial operations.
- Transaction validation checks whether incoming events match existing account and payment records.
- Monitoring and logging help identify suspicious requests, delivery failures, and processing errors.
Definition
Casino site webhook security refers to the authentication, integrity, validation, and processing controls used to protect automated event notifications between online casino infrastructure and external services.
A webhook is an HTTP-based notification that one application sends to another when a predefined event occurs. Unlike conventional API requests, which often retrieve information on demand, webhooks automatically deliver updates to a receiving system.
For example, a payment provider may send a notification indicating that a transaction has been completed. The receiving system must verify the notification before updating the corresponding account balance.
Related technical terms include webhook authentication, callback verification, webhook signature validation, and secure event processing. Although these terms describe different aspects of the process, they contribute to the same objective: protecting automated communication between connected systems.
How it works
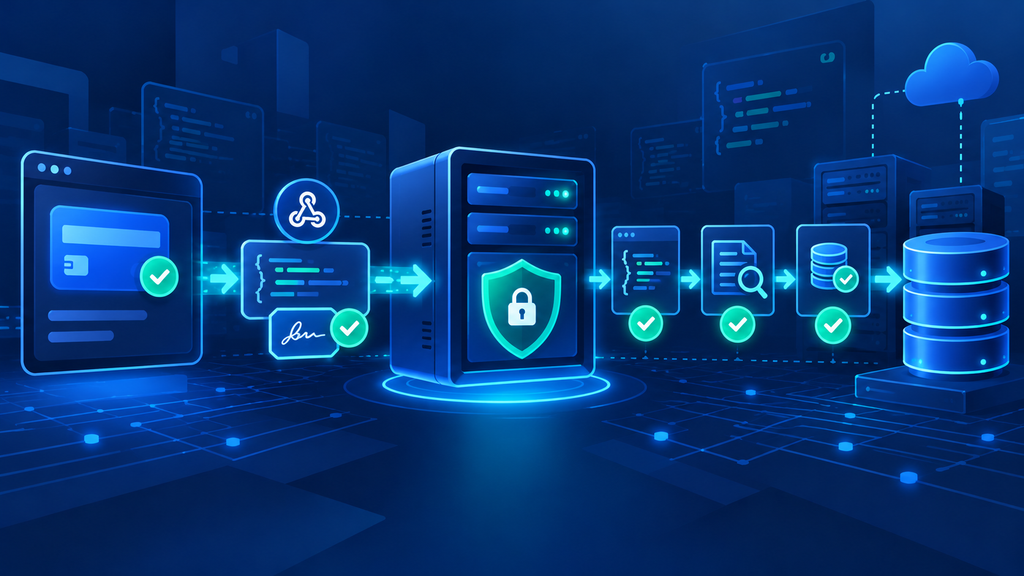
Casino site webhook security operates through several verification stages that protect incoming messages before they affect application data. These stages help determine whether an event originates from a trusted service, contains valid information, and can be processed without producing duplicate transactions.
A Connected Service Generates an Event
A webhook event begins when a connected system detects a relevant change. This may involve a payment transaction changing status, a refund being confirmed, a game transaction result becoming available, or an account-related event requiring synchronization.
The sending service generates an HTTP notification containing information about the event. Depending on the integration, this notification may include an event identifier, transaction reference, timestamp, and cryptographic signature.
These details allow the receiving application to identify the event and determine how it should be handled. However, receiving the message does not automatically establish that its contents are trustworthy.
The Receiving Server Verifies the Signature
Signature verification is a central component of casino site webhook security because it helps receiving servers distinguish authenticated messages from unauthorized requests.
A common authentication method uses a Hash-based Message Authentication Code (HMAC). The sender calculates a signature using a shared secret and the message data specified by its signing protocol. The receiving server independently calculates the expected signature.
If the supplied and expected signatures do not match, the notification is rejected. This helps protect against unauthorized messages and alterations to signed information.
Signature validation must follow the provider’s exact requirements, including message formatting, signed headers, and secret management. Implementations should also use constant-time signature comparison methods to reduce unnecessary exposure to timing-based attacks.
The System Checks Transaction Details
A valid signature does not automatically mean that a requested financial action should be performed. The receiving application must also validate the event against its internal records.
- Confirm that the transaction reference exists.
- Verify that the reported amount and currency match expectations.
- Check that the event belongs to the correct account.
- Confirm that the transaction status permits the requested update.
- Determine whether the notification has already been processed.
These checks help ensure that authentic notifications produce only authorized changes. For broader information about the underlying infrastructure, see how casino sites work in technology.
Duplicate Notifications Are Detected
Webhook providers may resend notifications when a receiving system fails to acknowledge delivery or experiences temporary processing problems.
This is why casino site webhook security must account for repeated notifications. A receiving application should not assume that every event will arrive exactly once.
An idempotent processing mechanism ensures that repeated delivery does not create additional financial effects.
For example, if a completed $50 transaction generates three identical notifications, the receiving system should record the financial effect only once. Unique transaction references, database constraints, and durable processing records can support this behavior.
Replay protection provides an additional safeguard by helping identify outdated or previously submitted messages. Depending on the provider’s protocol, authenticated timestamps and event identifiers may support this process.
The Event Is Processed and Recorded
Once the notification passes the required checks, the application processes the relevant operation. The system may update a transaction record, synchronize an account state, or record a completed event.
Processing results should be logged appropriately so technical teams can investigate errors and detect abnormal activity. A receiving server should also acknowledge deliveries according to the provider’s protocol.
Where appropriate, durable queues and background workers can separate event reception from slower downstream processing. This reduces unnecessary delivery timeouts while preserving the ability to investigate failed operations.
Why it matters
Webhook notifications can influence financial records and other sensitive application states. Without sufficient verification, an automated integration may process inaccurate, duplicated, or unauthorized instructions.
Casino site webhook security reduces these risks by requiring messages to pass authentication and transaction checks before processing. This provides an additional layer of protection between external notifications and internal application records.
If a receiving server accepts unverified notifications, an unauthorized party might attempt to submit a forged payment confirmation or modify event information. Repeated notifications also create operational risks when systems are not designed to handle duplicate delivery.
Secure event handling also supports record consistency between different services. For example, a payment provider and a gaming platform may maintain separate records of a transaction. Verification helps associate incoming notifications with the correct internal transaction and identify mismatched information.
However, these controls do not guarantee that every transaction or connected service is trustworthy. They protect specific stages of automated communication and should operate alongside broader application security measures.
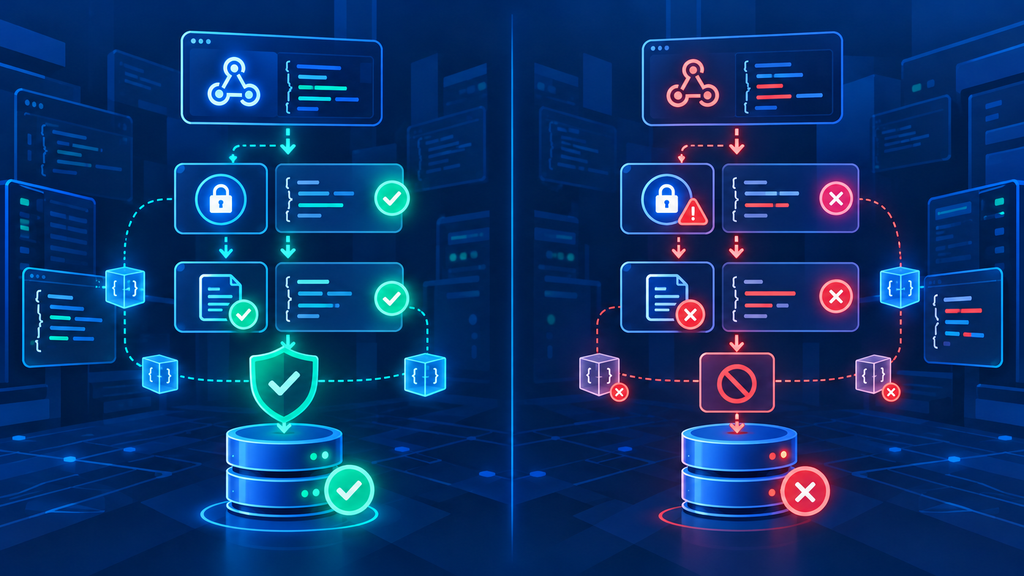
Casino Site Webhook Security Controls and Their Functions
Casino site webhook security relies on several complementary controls. Each addresses a particular weakness in automated communication, from message forgery to duplicate processing.
| Security Control | Primary Function | Example |
|---|---|---|
| HTTPS encryption | Protects information during transmission | Sending notifications over a TLS-encrypted connection |
| HMAC signature verification | Authenticates signed notifications and protects message integrity | Comparing a calculated signature with the received signature |
| Event validation | Confirms that notification data matches application records | Checking payment references, amounts, and account relationships |
| Replay protection | Helps identify previously submitted or outdated messages | Validating supported timestamps and event identifiers |
| Idempotent processing | Prevents duplicate financial operations | Recording a completed transaction only once |
| Monitoring and logging | Supports error detection and incident investigation | Recording rejected notifications and delivery failures |
These safeguards should be adapted to the requirements of the specific webhook provider and receiving application. No individual control replaces the need for appropriate transaction validation and secure credential management.
Common mistakes and misconceptions
Misunderstanding the responsibilities of webhook authentication and transaction processing can create avoidable security weaknesses.
HTTPS Alone Makes Webhooks Secure
HTTPS encrypts data in transit, but encryption does not automatically establish that the sender is authorized. A receiving server still needs to authenticate the notification and validate its contents.
A Valid Signature Guarantees a Valid Transaction
A valid signature provides evidence about message authenticity and integrity within the applicable signing protocol. It does not prove that every transaction detail is appropriate or that the event should change an account balance.
Every Webhook Notification Is Delivered Exactly Once
Webhook delivery systems may retry messages after timeouts or temporary failures. Applications should not assume that every notification will arrive exactly once. Idempotent processing helps prevent these retries from producing repeated financial effects.
Replay Protection and Duplicate Detection Are Identical
Replay protection helps identify reused or outdated messages, while duplicate detection prevents previously handled events from triggering repeated operations. Authenticated timestamps may help limit replay attempts, but durable transaction records remain important.
Signature Verification Removes the Need for Monitoring
Even correctly authenticated notifications can fail during database processing or encounter invalid transaction states. Logging, error monitoring, and reconciliation remain necessary.
Understanding these distinctions is important because casino site webhook security depends on multiple safeguards working together rather than a single authentication method.
Examples
The following scenarios illustrate how secure webhook handling protects automated transactions under different conditions.
Forged Payment Confirmation
An unauthorized sender attempts to submit a notification claiming that a transaction has been completed. The receiving server checks the cryptographic signature using the expected secret.
Because the forged message does not contain a valid signature, the notification is rejected before any financial record is updated. This demonstrates how casino site webhook security can prevent an unauthenticated message from initiating a transaction change.
Duplicate Deposit Notification
A payment service sends a legitimate notification, but the receiving server experiences a temporary acknowledgment failure. The provider retries the same event.
The system recognizes the transaction identifier and determines that the financial operation has already been completed. The repeated notification is handled without applying another balance adjustment.
Valid Message With Incorrect Transaction Details
A notification passes signature verification but contains a transaction reference or amount that does not match the receiving application’s records.
The server declines to perform the requested account update and records the inconsistency for investigation. This demonstrates why message authentication and transaction validation are separate requirements.
Across these examples, casino site webhook security serves the same technical purpose: ensuring that received notifications are evaluated before changes are committed to application records.
FAQ
What is the main purpose of casino site webhook security?
Its main purpose is to ensure that automated notifications are authenticated, validated, and processed safely. These controls help prevent forged events, unauthorized state changes, and duplicate financial operations.
Can webhook signature verification prevent all transaction fraud?
No. Signature verification helps establish message authenticity and integrity, but it does not independently confirm that a transaction is legitimate. Secure processing also requires transaction validation, access controls, monitoring, and appropriate financial reconciliation.
Why is idempotency important for casino webhook transactions?
Idempotency prevents repeated notifications from causing the same financial operation to be performed more than once. It is particularly important because webhook providers may resend legitimate events after delivery failures, timeouts, or temporary network disruptions.
Resources
- OWASP. Webhook Security Cheat Sheet
- Adyen. Verify HMAC Signatures
- Adyen. Secure Webhooks
- Adyen. Handle Webhook Events
- GitHub. Best Practices for Using Webhooks
- GitHub. Validating Webhook Deliveries